
Sitemize üye olarak beğendiğiniz içerikleri favorilerinize ekleyebilir, kendi ürettiğiniz ya da internet üzerinde beğendiğiniz içerikleri sitemizin ziyaretçilerine içerik gönder seçeneği ile sunabilirsiniz.
Sitemize üye olarak beğendiğiniz içerikleri favorilerinize ekleyebilir, kendi ürettiğiniz ya da internet üzerinde beğendiğiniz içerikleri sitemizin ziyaretçilerine içerik gönder seçeneği ile sunabilirsiniz.
Üyelerimize Özel Tüm Opsiyonlardan Kayıt Olarak Faydalanabilirsiniz
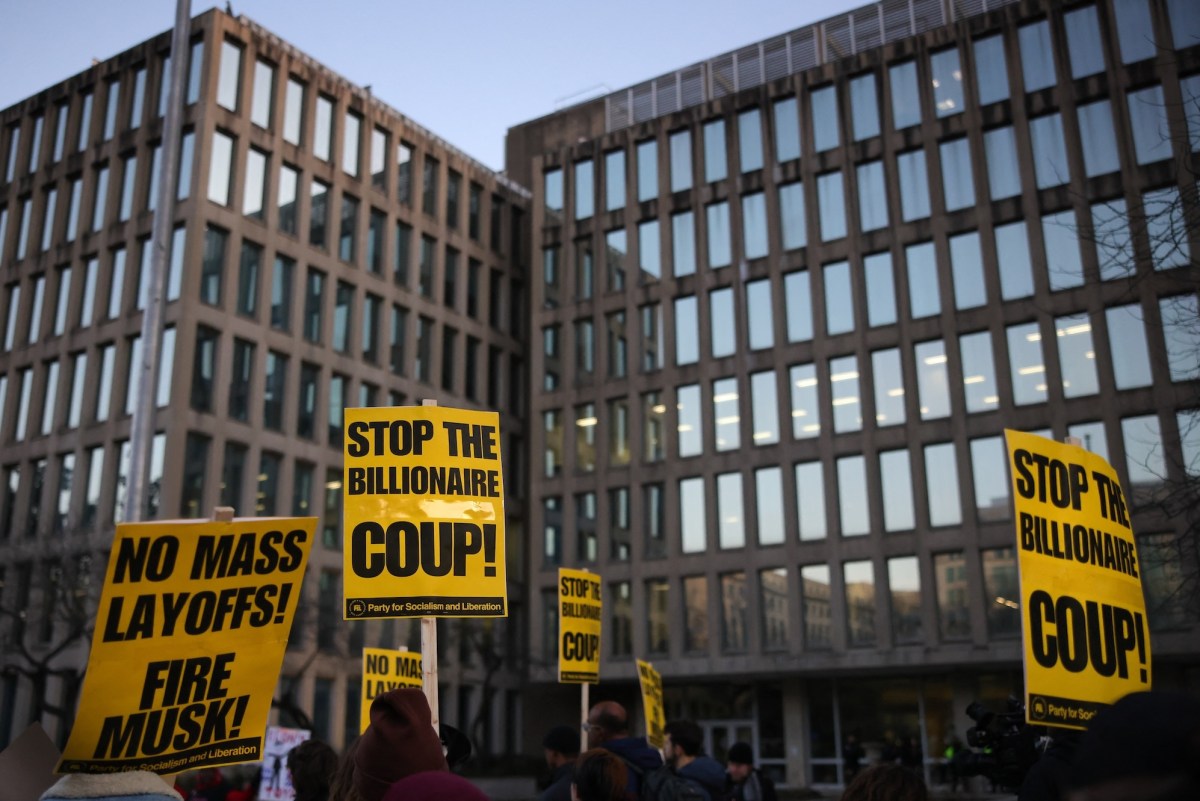
The year 2026 has already earned a notorious reputation in the cybersecurity community, marked by a string of high‑profile attacks that exposed the fragility of both private and public digital assets. Among the most consequential incidents are the massive DOGE data breach, a wave of critical‑infrastructure compromises, and a bold intrusion into United States federal surveillance networks.
In early April, the cryptocurrency platform DOGE announced that a database containing over 150 million user records had been exfiltrated. The stolen data set included email addresses, hashed passwords, and, alarmingly, a subset of wallet private keys. The breach forced exchanges worldwide to tighten their security protocols, accelerate the rollout of mandatory two‑factor authentication, and re‑evaluate how they store cryptographic secrets.
May saw a cascade of attacks on essential services. A European power‑grid operator fell victim to a ransomware campaign that leveraged a previously unknown vulnerability in its SCADA environment. The attackers demanded a multi‑million‑dollar ransom, and the resulting outage left millions without electricity for several hours. Simultaneously, a major water‑treatment facility in Southeast Asia experienced a similar intrusion: threat actors manipulated sensor data, temporarily disabling quality‑control mechanisms. Both incidents underscored the growing risk that legacy industrial control systems pose when they lack modern patch management and network segmentation.
The most politically charged event unfolded in July, when a sophisticated hacking group breached several U.S. federal surveillance platforms. The intruders gained access to phone‑metadata archives, location‑tracking databases, and even classified operational reports. The breach prompted an emergency congressional hearing and accelerated the deployment of zero‑trust architectures across intelligence agencies.
Taken together, these three incidents illustrate a stark reality: cyber threats now target the financial sector, essential public utilities, and national security apparatus with equal ferocity. Security analysts warn that organizations must move beyond reactive patching toward continuous threat‑modeling, regular red‑team exercises, and comprehensive employee training. As governments draft new cyber‑resilience legislation and tech firms roll out AI‑driven defense tools, the second half of 2026 promises to be a pivotal period for shaping the next generation of digital safeguards.
Source: TechCrunch
 ETİKETLER
 BENZER İÇERİKLER
 OKUYUCU YORUMLARI
2026’s Biggest Hacks: From DOGE Breach to Federal Surveillance Takeover



Yorum Yaz