
Sitemize üye olarak beğendiğiniz içerikleri favorilerinize ekleyebilir, kendi ürettiğiniz ya da internet üzerinde beğendiğiniz içerikleri sitemizin ziyaretçilerine içerik gönder seçeneği ile sunabilirsiniz.
Sitemize üye olarak beğendiğiniz içerikleri favorilerinize ekleyebilir, kendi ürettiğiniz ya da internet üzerinde beğendiğiniz içerikleri sitemizin ziyaretçilerine içerik gönder seçeneği ile sunabilirsiniz.
Üyelerimize Özel Tüm Opsiyonlardan Kayıt Olarak Faydalanabilirsiniz
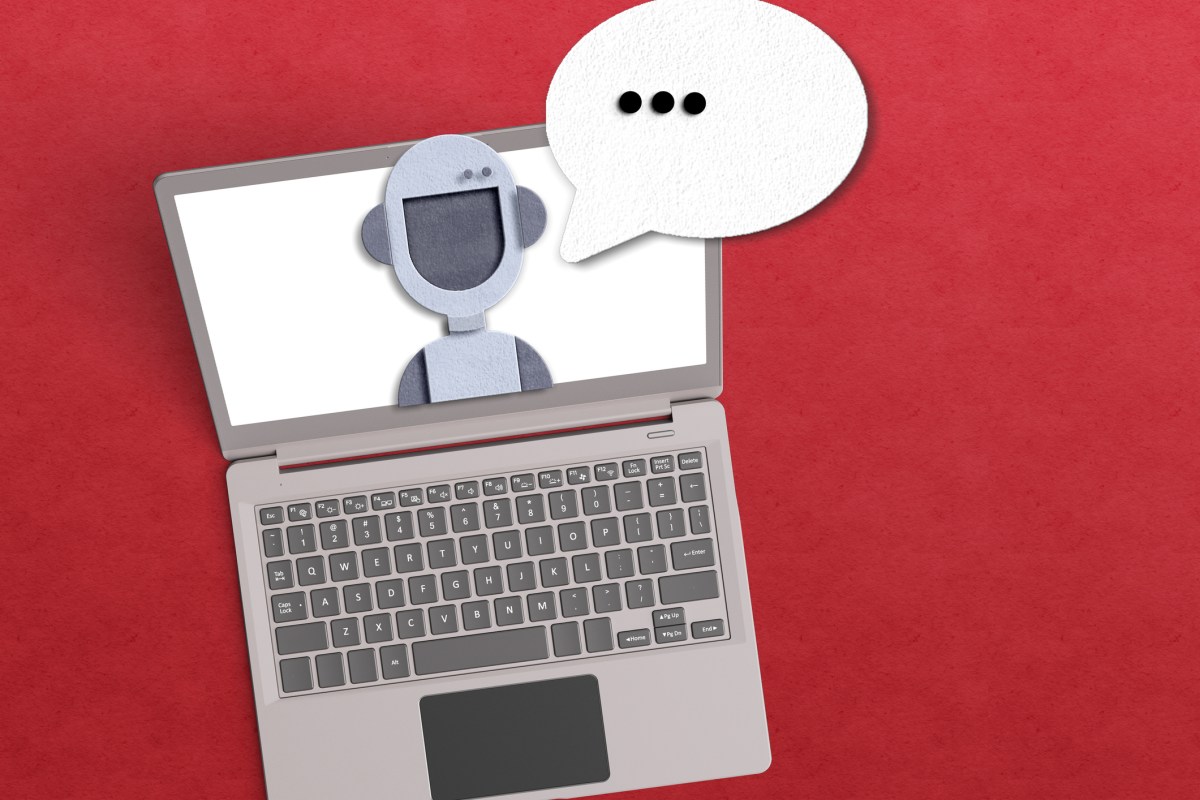
Security analysts have uncovered that the AI‑driven penetration testing platform Artex is openly reachable on hundreds of internet‑facing servers. The researchers say that misconfigurations left the tool’s web interface and command‑line endpoints exposed, allowing anyone—including malicious actors—to launch automated scans and exploit discovery with a single click.
Artex is marketed to security teams as a sophisticated assistant that uses machine learning to identify vulnerabilities faster than traditional scanners. While its capabilities can accelerate defensive testing, the lack of proper access controls turns the tool into a potent weapon in the hands of attackers. After detecting the issue, the research team followed responsible disclosure procedures, notifying the server owners and prompting many of them to shut down public access within hours.
The incident highlights how easy it is for critical security utilities to become an attack surface when cloud or on‑premise configurations are overlooked. Experts recommend enforcing strict authentication, limiting inbound traffic through firewalls, and regularly auditing exposed services. Continuous monitoring and automated compliance checks can also help spot such gaps before they are exploited.
The public exposure of Artex serves as a cautionary tale for organizations that rely on advanced security software. Companies should treat the tools themselves as sensitive assets, applying the same hardening practices used for any other critical infrastructure. By tightening permissions, employing network segmentation, and keeping an eye on unusual usage patterns, organizations can mitigate the risk of their own defensive tools being turned against them.
Source: TechCrunch
 ETİKETLER
 BENZER İÇERİKLER
 OKUYUCU YORUMLARI
Hundreds of Artex AI Penetration Tools Exposed Online



Yorum Yaz